From Cyber Incident Reports to Ongoing Maintenance, the Story Behind a CSIRT Portal for Banking
Banks hold the two things cybercriminals want most, money and customer data. Almost every day brings phishing attempts, fake websites imitating bank services, and security gaps reported by outside parties. The question is no longer whether an incident will happen, but how quickly a bank can receive a report, handle it, and inform the public.
This is why many financial institutions set up a Computer Security Incident Response Team, or CSIRT, a team responsible for receiving, handling, and coordinating responses to cyber security incidents. A team like this needs more than an email address. It needs an official reporting channel, well-kept handling records, and a way to share security information.
That was the need a regional development bank in Sulawesi brought when it contacted Aistech.
The Need on the Table
The bank already had a team handling information security, but it did not yet have a portal to serve as that team’s official face. Incident reports could come from anywhere, and without a single entry point it was hard to make sure every report was recorded, handled, and clearly closed.
Early discussions narrowed the bank’s needs down to three things. An official channel for anyone to report an incident. A tool for the team to manage every report through to resolution. A space to publish security advisories and information for customers and the public.
Turning a Proposal into a Working System
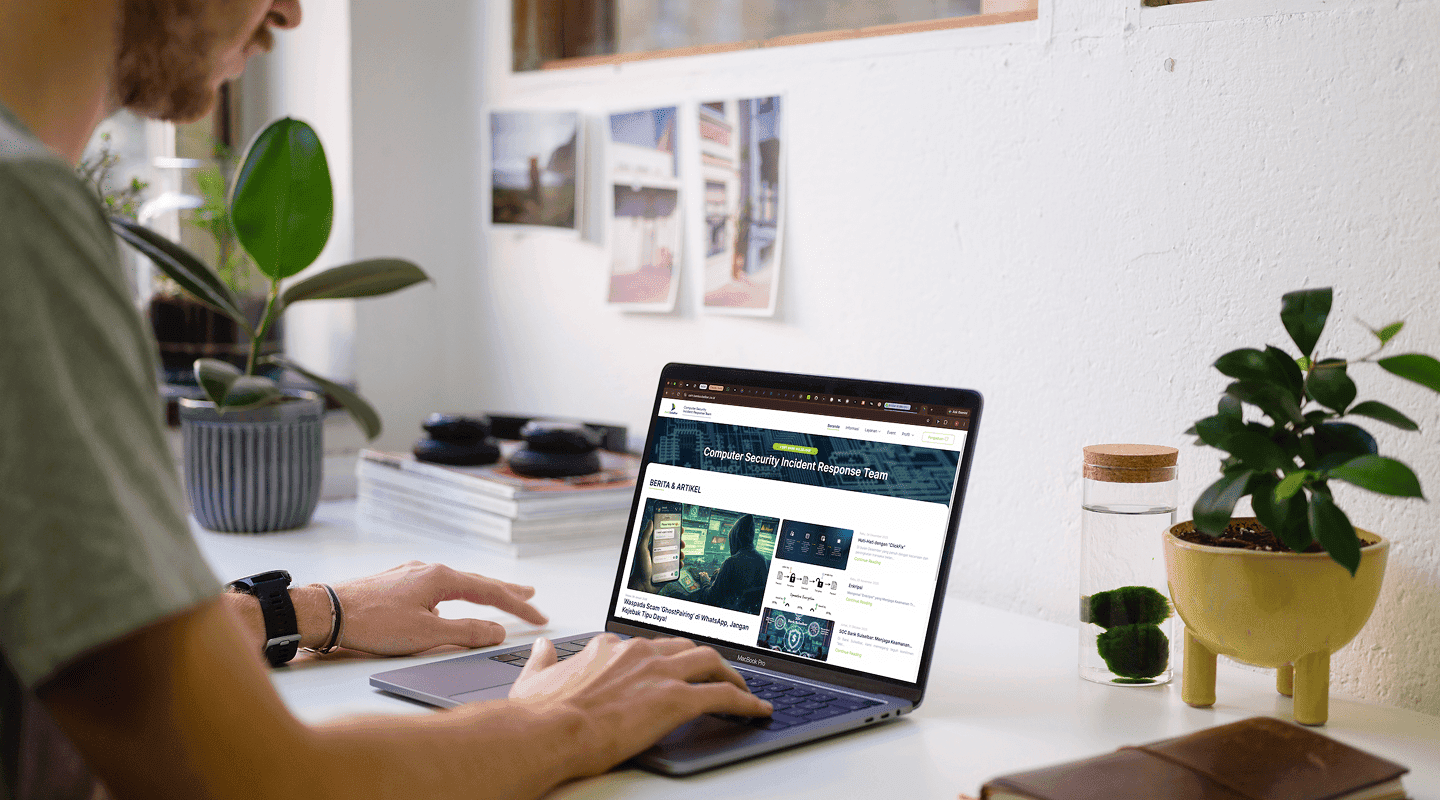
Aistech put together a proposed solution, then built it from interface design through to the system behind it. The core features follow common CSIRT practice and were then adapted to banking workflows and standards. The result is a portal with three main parts.
Trackable Incident Tickets
Reporters fill in a form and attach supporting evidence. Every report receives a ticket number sent to the reporter’s email, so its progress can be followed without having to ask again and again.
Documented Handling
The CSIRT team works from a single dashboard showing report counts and statistics. Each ticket moves from Opened, On Progress, and Pending to Closed, and every status change is recorded along with its handling notes. This trail matters when the bank needs to account for how an incident was handled.
Security Information for the Public
The portal also serves as the bank’s security information hub. The team can publish security advisories, monthly and annual monitoring reports, news and articles, event schedules, and the RFC 2350 document, a standard profile that describes the team, its scope, and its services.
Handover Is Not the End of the Story
Once the system was completed and handed over, the bank’s CSIRT team began using the portal. But a security system cannot simply be left to run on its own. Threats change, the team’s needs grow, and daily operations keep producing new findings.
So the bank continued the partnership through regular maintenance. Roughly every quarter, the Aistech team visits on site to follow up on findings from CSIRT operations, from fixes and adjustments to any development that is needed. With this arrangement, the bank does not need to build its own development team to keep the system relevant.
What Sets It Apart
1. One entry point for every report. Every incident comes in through the same channel and is immediately recorded as a ticket.
2. A complete handling trail. Every status change and note is stored, so incident handling can be accounted for at any time.
3. Reporters are not left waiting in the dark. A ticket number lets reporters follow the progress of their own report.
4. Public communication from the same team. Advisories, monitoring reports, and RFC 2350 are published from the same portal used to handle incidents.
5. Adapted for banking. Common CSIRT practice is translated into the workflows and standards that apply in a bank.
6. Support after handover. Regular on-site maintenance makes sure findings in the field are followed up quickly.
Closing
A CSIRT portal is more than a complaint application. It is how an organization shows that every incident report is received, handled, and accounted for. For a bank, that ties directly to customer trust.
The same foundation can be adapted for other institutions that need an incident response team, such as local governments, universities, and state-owned enterprises. Service categories, handling statuses, and portal content can follow each organization’s procedures, and when there are specific needs, features can be developed so the system follows how the team works.
